NOVA Compliance
Build Trust. Prove Compliance. Move Forward.
NOVA Compliance brings compliance management, evidence, controls and human decisions together in one governed workspace for growing and regulated organisations.
NOVA accelerates your launch preparation, but final decisions remain human.
Illustrative demo data. Readiness percentages are examples, not customer results.
AI Governance
AI governance with human oversight
NOVA supports AI governance with governed controls, policies and evidence: explain requirements, draft descriptions, summarise artefacts and identify likely gaps while keeping human oversight in the approval loop. You're in control.
- Interprets and summarises uploaded evidence
- Prepares policy and control description drafts
- Identifies likely gaps against activated requirements
- Explains what a requirement is asking for in plain language
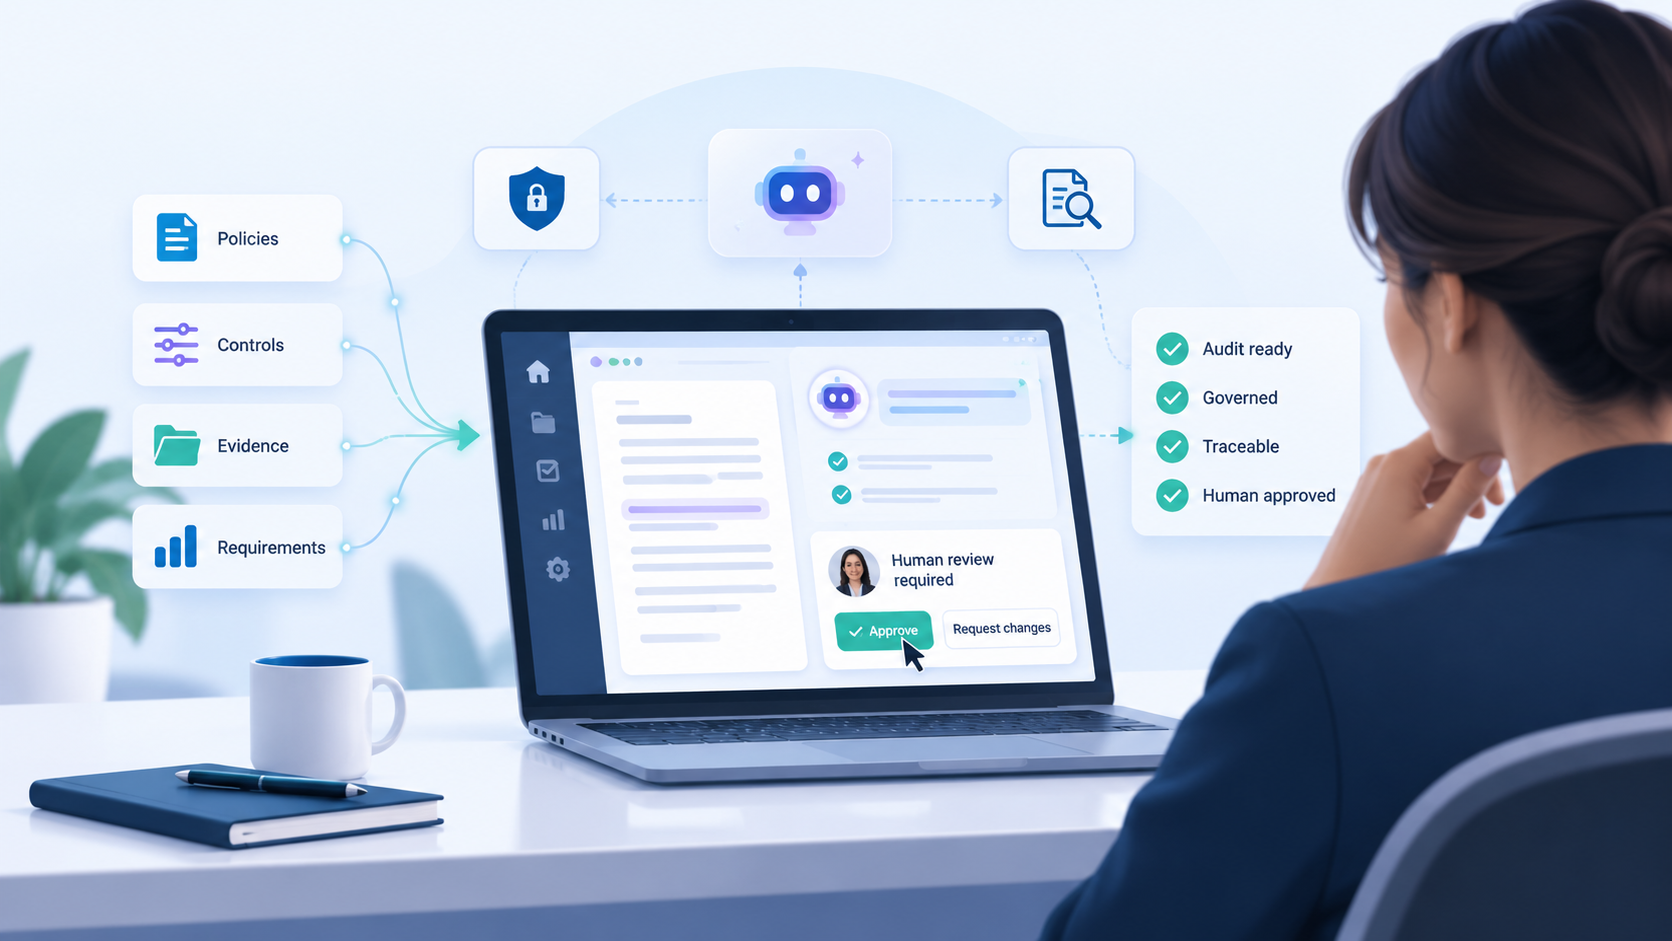
“NOVA accelerates your launch preparation, but final decisions remain human.”
What NOVA does: Supports and accelerates compliance readiness preparation by helping organise evidence, identify gaps, and inform decision-making.
What you control: You retain final authority and accountability for policy approvals, risk acceptance, launch decisions, and all statements made to auditors, regulators, or customers.
Who NOVA is for
Built for the people responsible for trust
Whether you're establishing your first compliance program or managing governance across an enterprise, NOVA adapts to the way you work.
Founders & growing teams
Get compliance under control without building an enterprise-sized compliance department.
Explore NOVA for growing teams
Compliance & risk teams
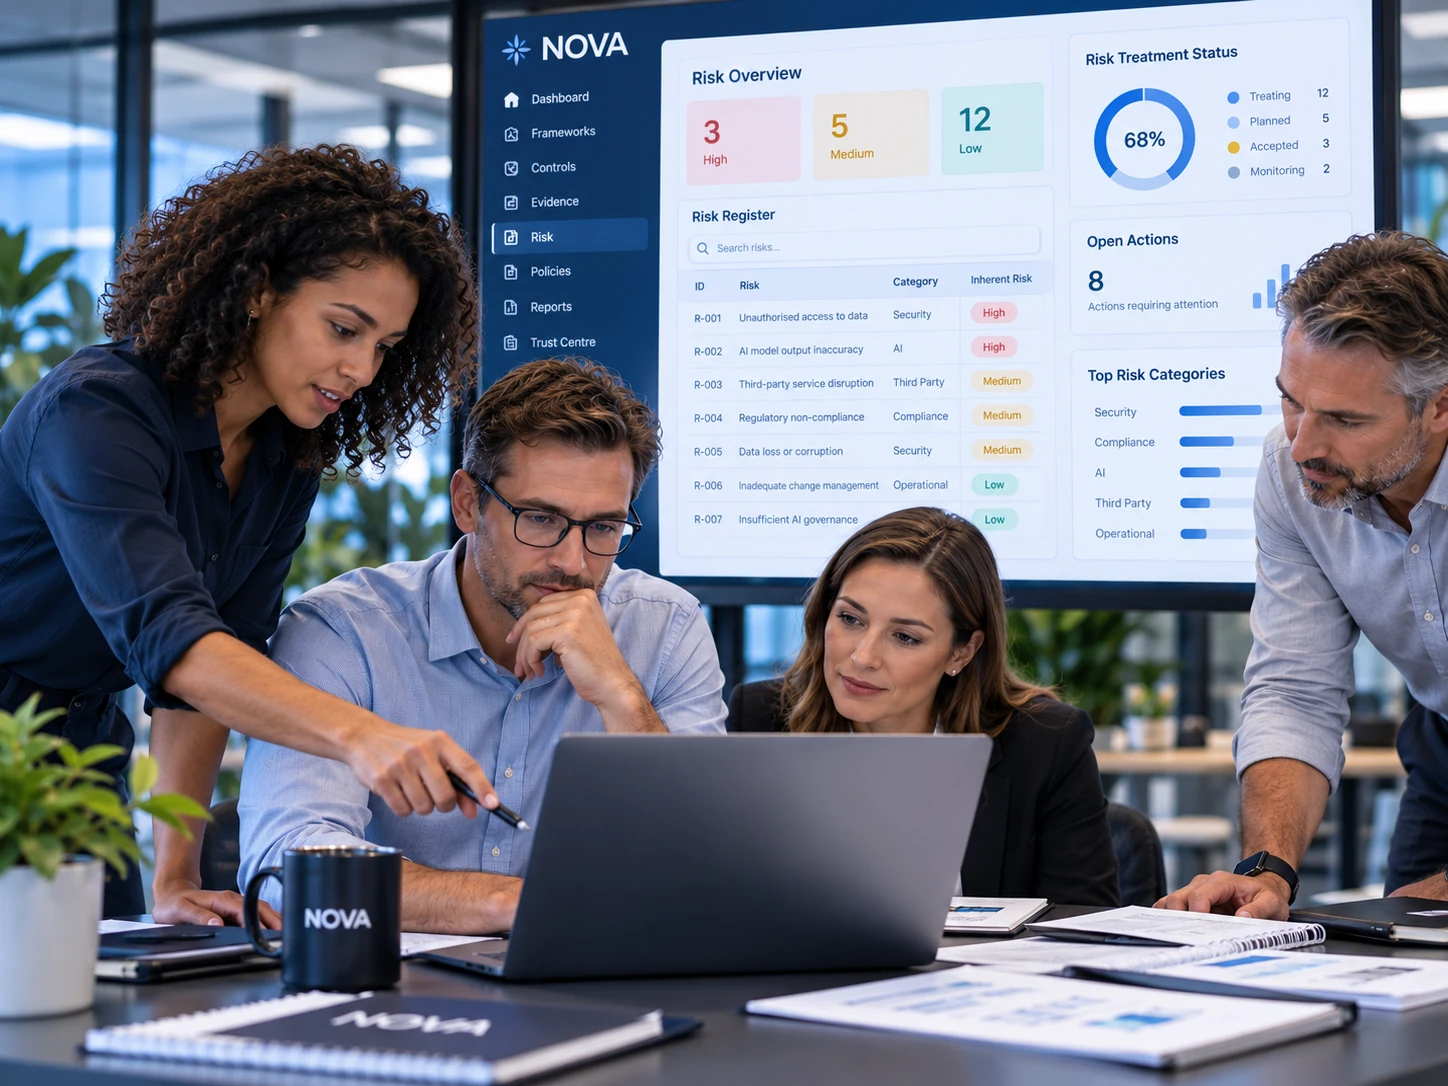
Bring frameworks, controls, evidence, policies and risk together in one connected platform.
Explore NOVA for compliance teams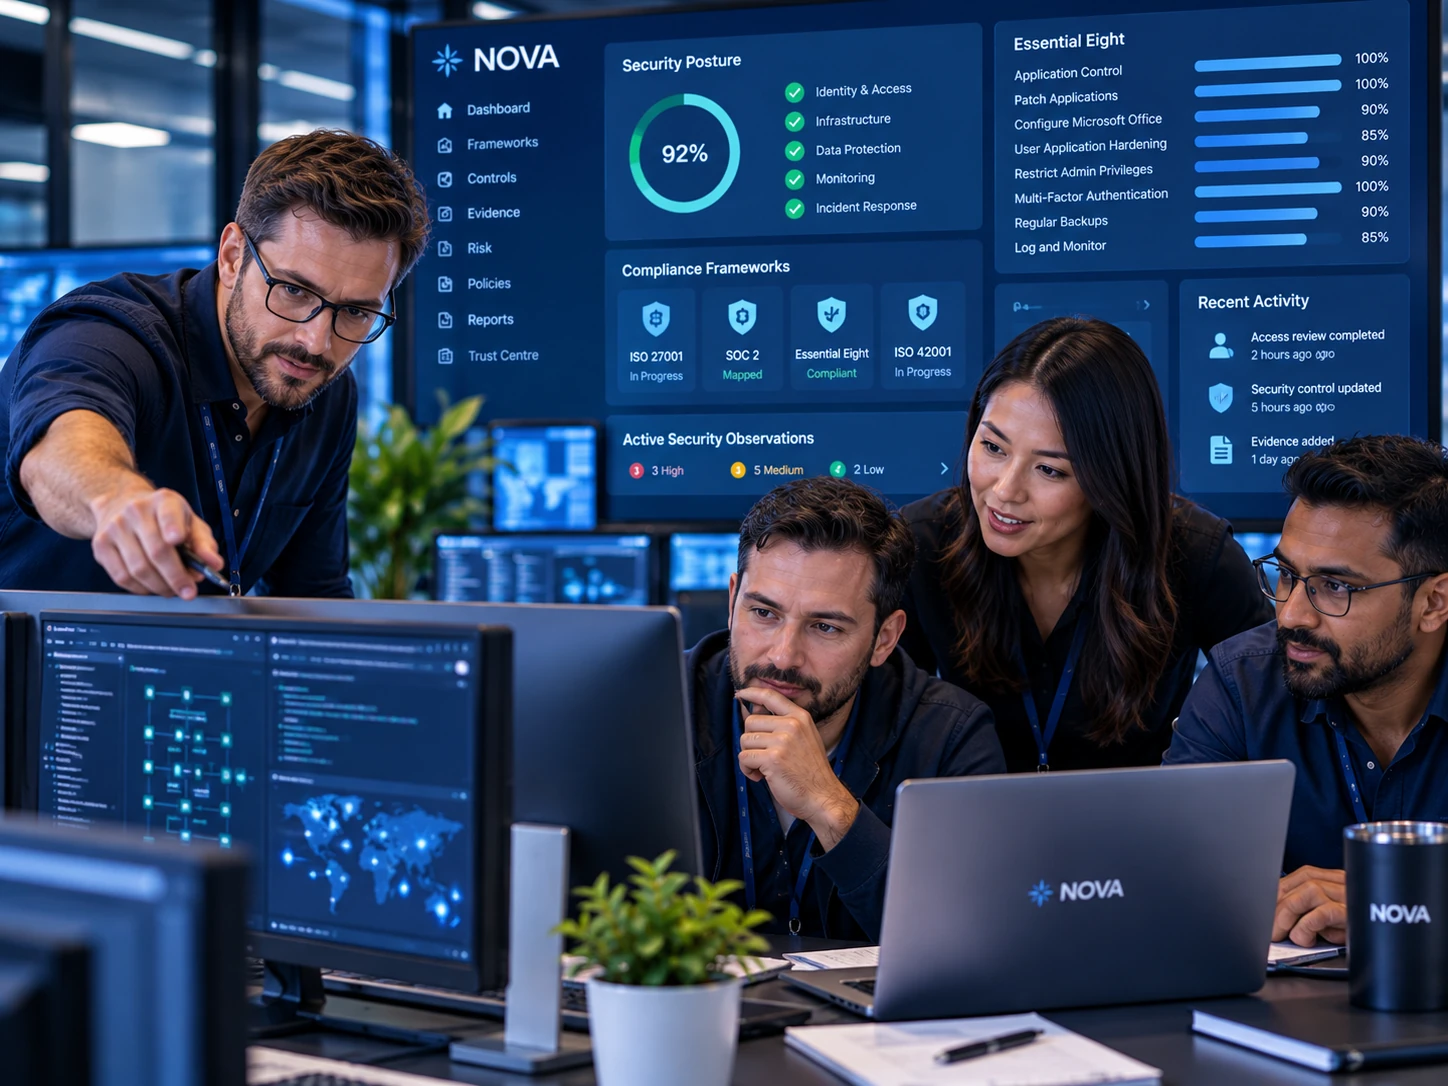
Security & technology teams
Connect technical security work with the evidence and controls your organisation needs to demonstrate compliance.
Explore NOVA for security teams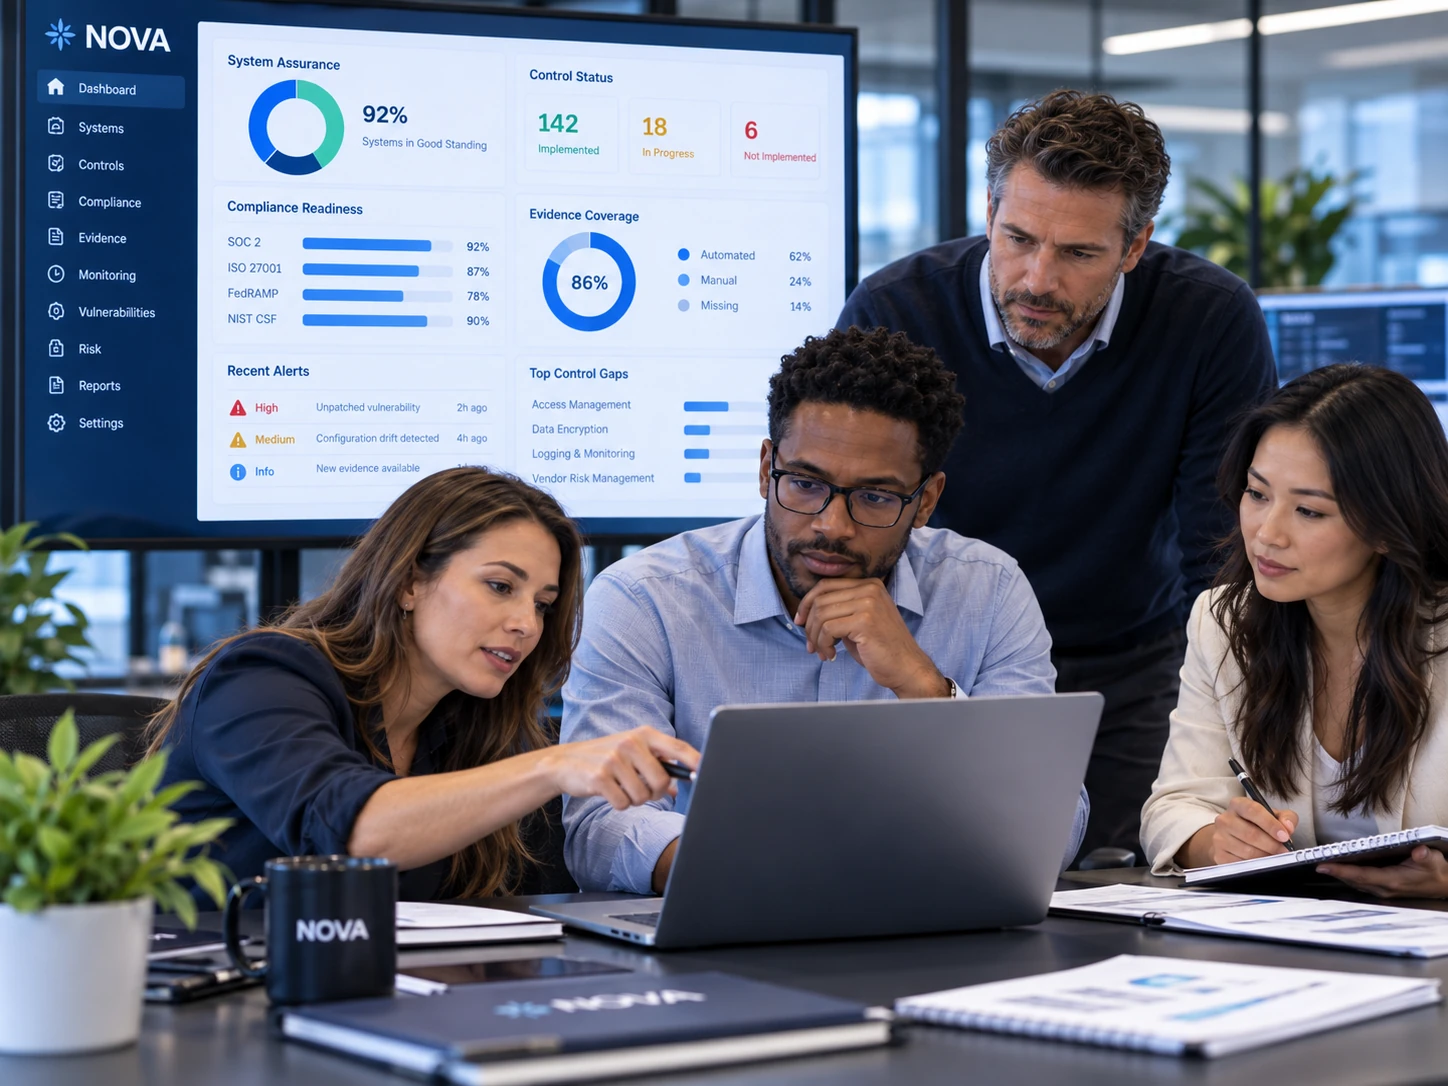
Auditors & assurance
Review controls, evidence and compliance status without chasing spreadsheets, folders and email trails.
Explore NOVA for assuranceWhy NOVA
Compliance shouldn't live in disconnected systems
NOVA keeps the compliance management record together so teams can spend less time assembling status and more time on accountable decisions.
One connected compliance system
Frameworks, controls, policies, evidence, risk and reporting work together.
Reuse work across frameworks
Where controls and evidence overlap, NOVA helps reduce unnecessary duplication.
Know where you stand
See compliance progress, evidence coverage, risks and gaps without assembling the picture manually.
AI-supported. Human-governed.
Use AI to assist the work while preserving human accountability for compliance and risk decisions.
Built to grow with you
Start with current requirements and expand governance capability as needs grow.
Product proof
See compliance as it happens
The claims above are grounded in a working product: one governed workspace for frameworks, controls, evidence, policy, risk, reporting and assurance.
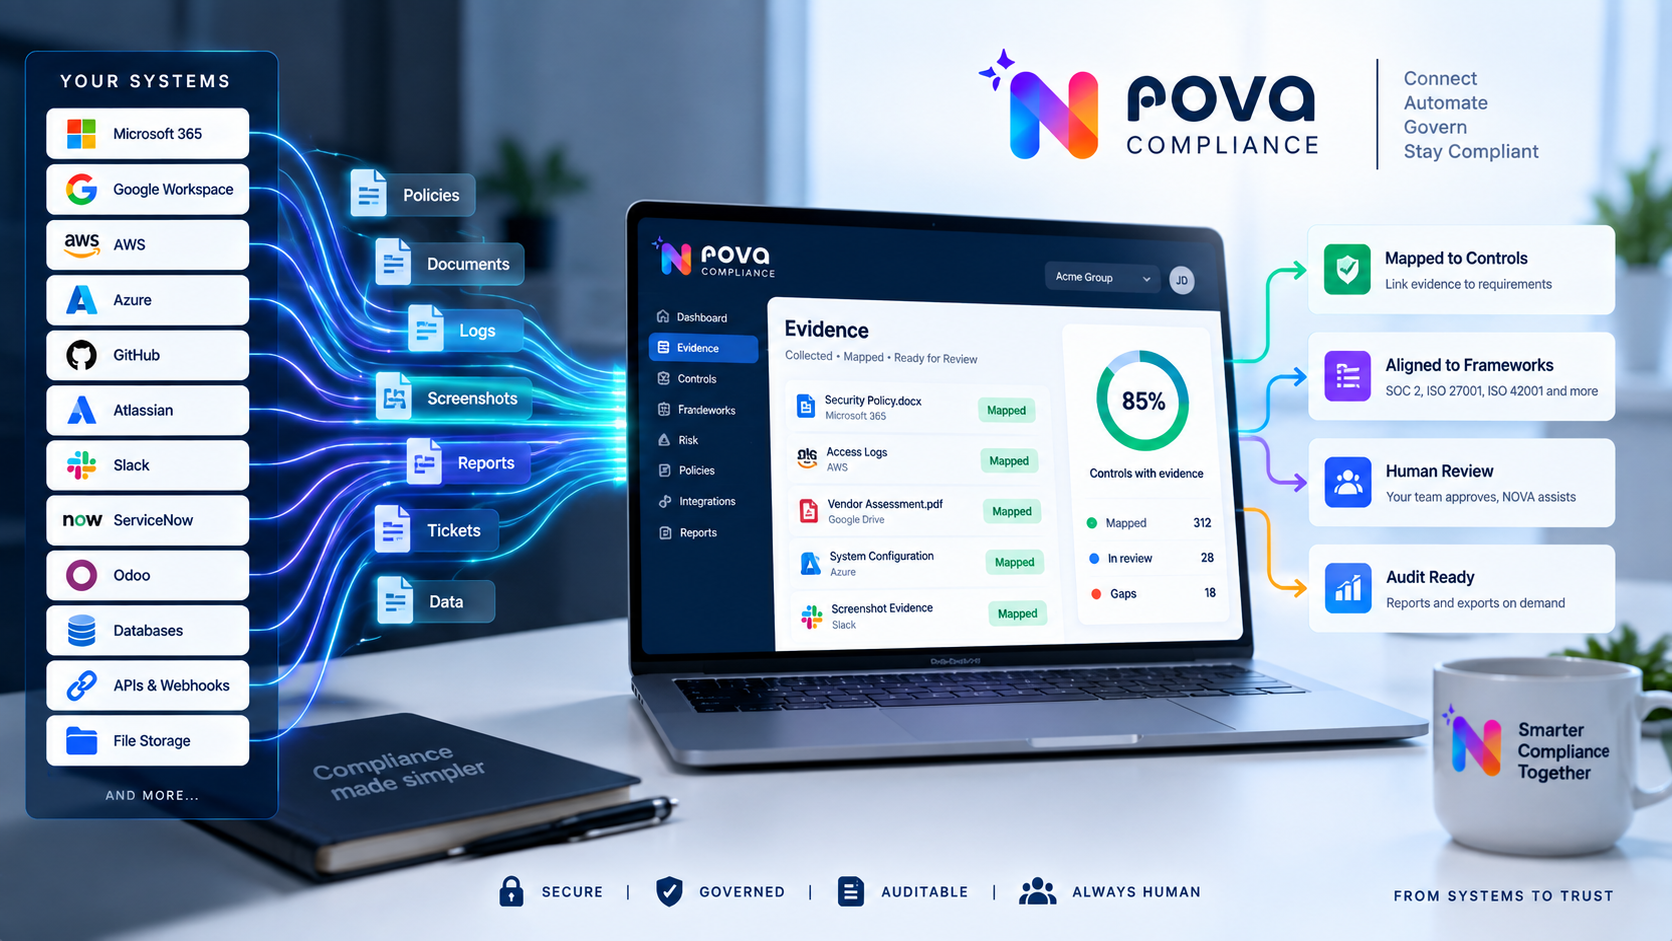
Frameworks
Scope requirements and connect them to the controls your organisation actually operates.
Controls & evidence
Collect evidence with context, map it to controls and keep reviewer validation visible.
Policies & risk
Keep policy approvals, risks, assets and accountability connected to the programme record.
Reports & assurance
Use live records to support readiness reporting, Trust Centre publication and scoped auditor access.
Frameworks
- SOC 2
- ISO 27001
- Essential Eight
- ISO 42001
Controls
- Mapped expectations
- Owners
- Test cadence
Evidence
- Uploads
- Connectors
- Reviewer validation
Assurance
- Readiness reporting
- Trust Centre
- Auditor Portal
Frameworks
SOC 2 readiness and multi-framework compliance
27 framework capabilities are represented in the governed NOVA catalogue. The public cards distinguish what is available now from what is available by configuration; activation still depends on customer scope and evidence.
SOC 2
Available nowService organisation reporting against the Trust Services Criteria, used widely in enterprise procurement.
ISO/IEC 27001
Available nowThe international standard for an information security management system, certified by an accredited body.
Essential Eight
Available nowEight prioritised mitigation strategies published by the Australian Cyber Security Centre, assessed by maturity level.
ISO/IEC 42001
Available nowThe management system standard for artificial intelligence, covering governance of AI systems across their lifecycle.
GDPR — General Data Protection Regulation (EU) 2016/679
Available by configurationRegulatory privacy requirements for organisations handling personal data in the EU/EEA and related contexts.
PCI DSS v4.0.1 — Payment Card Industry Data Security Standard
Available by configurationPayment-card security readiness for environments that store, process or transmit cardholder data.
HIPAA — Privacy, Security & Breach Notification
Available by configurationUS healthcare privacy, security and breach-notification readiness for covered entities and business associates.
Cybersecurity Maturity Model Certification (CMMC)
Available by configurationUS defence-industrial cybersecurity readiness across CMMC practices, scope, evidence and assessment preparation.
Custom framework available
Create a custom framework for any requirement.
Bring customer, contractual, regulatory or internal requirements into a governed framework with human-reviewed mappings and evidence decisions.
Discuss your requirementsIllustrative readiness snapshot
Illustrative interface concept. Values shown are examples, not customer data.
Readiness
Readiness
Maturity coverage
Readiness
Choose your next step
What are you trying to achieve?
Start with the outcome you need, then follow the path that best matches your current compliance work.
Get compliance ready
Build a structured compliance program and understand what still needs attention.
Explore this pathPrepare for an audit
Organise controls, evidence and supporting information before assurance begins.
Explore this pathManage multiple frameworks
Reduce duplicated work and understand where requirements overlap.
Explore this pathBuild stronger governance
Bring compliance, policies, risk, evidence and accountability together.
Explore this pathSecurity and trust
Trust starts with how the platform itself is governed
NOVA keeps each organisation's evidence inside its own tenant boundary, with role-based access, human oversight and scoped auditor engagement.
- Tenant-isolated workspaces
- Role-based access inside each tenant
- Scoped Auditor Portal access per engagement
- Published security practices, not unverified claims
FAQ
Common questions
Browse concise answers about NOVA, frameworks, evidence, AI, security and pricing.
What does NOVA actually do that spreadsheets and shared folders do not?
NOVA connects requirements, controls, evidence, owners and readiness reporting as governed records, so changes and gaps can be traced instead of being scattered across spreadsheets and folders.
Pricing
Start where you are. Scale when you're ready.
From organisations beginning their compliance journey to teams managing complex multi-framework governance, NOVA provides a clear path to grow.
Start
For organisations beginning their compliance journey.
Grow
For teams managing more frameworks, repositories and users.
Scale
For organisations requiring broader governance and enterprise capability.
Ready to see what your compliance program looks like in NOVA?
Explore the platform, compare plans or speak with us about your compliance requirements.
NOVA accelerates your launch preparation, but final decisions remain human.